

The Vibecoding Disaster: 04 Surprising Truths from the Mercor AI Data Breach


By Jin, Founder & Startups
, updated 8 min read
The 40-Minute Meltdown
We have entered an era where we outsource our professional identities to black boxes and call it progress. We trust our AI gateways and security tools implicitly, treating them as bulletproof shields.
The Mercor AI breach provides a sobering autopsy of how fragile that trust truly is.
Mercor AI, a platform valued in the billions and designed to connect experts to titans like OpenAI and Anthropic was crippled in less than an hour. A supply chain attack that lasted a mere 40 minutes managed to compromise a company facilitating over $2 million in daily payouts.
This was a high-speed wreck in the heart of the AI gold rush. We assumed the gatekeepers were secure because they were expensive. But boy we were wrong...
The 40-Minute Domino Effect
The breach was not a direct frontal assault on Mercor’s fortress but a case of "upstreaming the poison."
According to Unit 42, the threat group TeamPCP compromised the PyPI publishing credentials for the LiteLLM library. LiteLLM isn't some obscure script; it boasts over 95 million monthly downloads and serves as a critical routing gateway for AI applications.
Malicious versions (1.82.7 and 1.82.8) were live for only 40 minutes, yet the scale was staggering. Wiz estimates that this brief window potentially impacted 500,000 machines across 36% of all cloud environments. In modern cyberwarfare, data exfiltration happens in under 60 seconds once the malware executes.
The attack effectively turned the tools meant to protect infrastructure into the vehicles for its destruction. By the time a human could even blink at a dashboard, the keys to the kingdom were already gone.
"Unlike past supply chain attacks, this operation explicitly weaponizes security and developer infrastructure that inherently require elevated privileges. This allows attackers unimpeded access to production secrets." — Unit 42 Report
Why Compliant Doesn't Mean "Secure"
In the fallout, a heated debate ignited on Hacker News regarding Mercor’s security "pedigree."
The company had undergone verification by a legitimate audit firm yet this failed to prevent a total exfiltration of 4 TB of data. This underscores what skeptics call the "liability transfer framework", the idea that SOC2 and ISO27001 are often just forms of compliance cosplay used to lower insurance premiums.
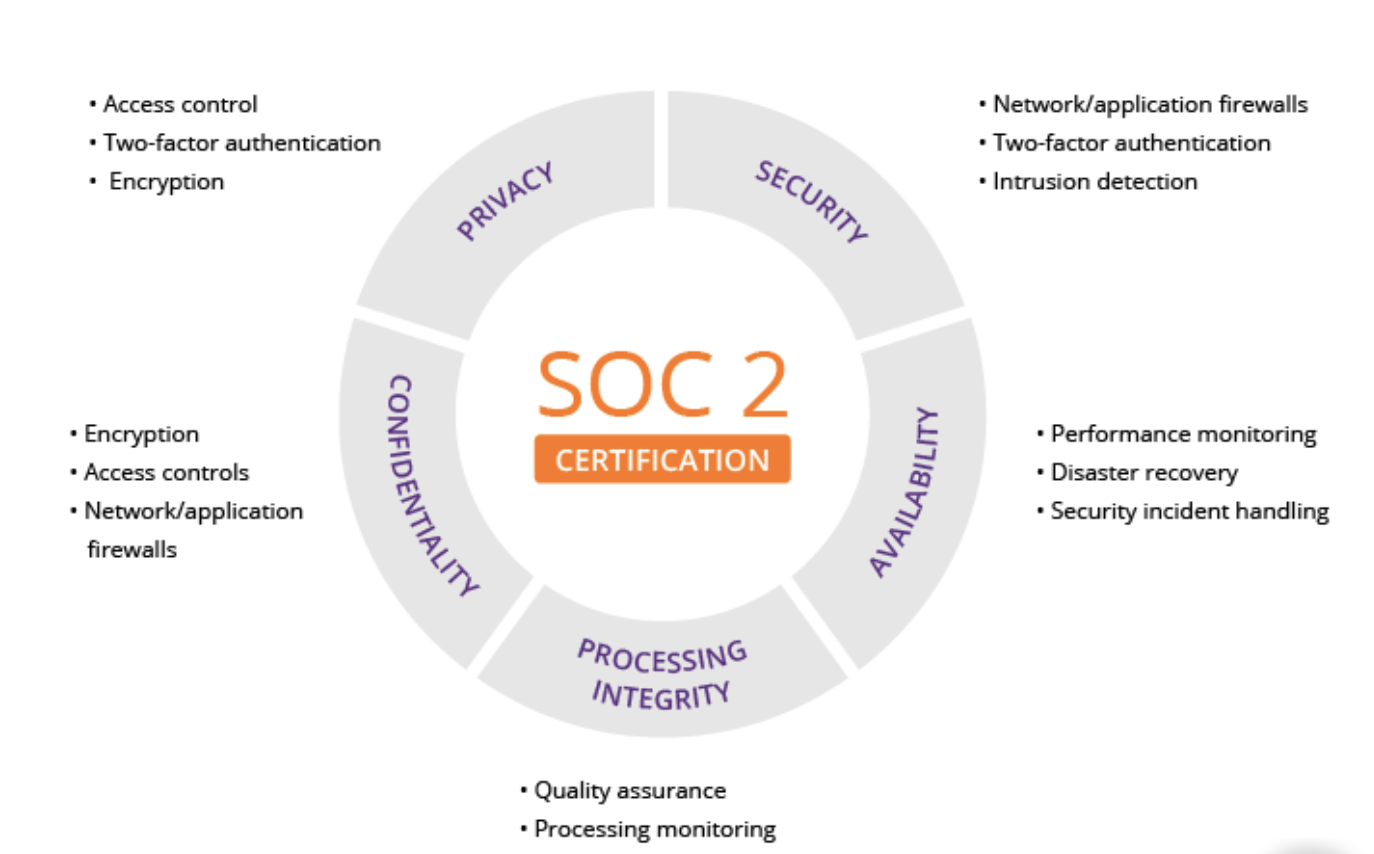
Audits are about checking boxes but security is about stopping bullets. The theft of 4TB comprising 939GB of source code, 211GB of databases, and 3TB of storage buckets proves that a certificate on the wall is not a firewall.
Compliance: A standardized method for communicating activity to outside parties to satisfy insurance and contract requirements.
Capability: The technical rigor required to defend against 0-day supply chain attacks and maintain actual infrastructure integrity.
The Privacy Nightmare
The breach was a wholesale theft of human identity.
Of the 4TB stolen, 3TB consisted of storage buckets containing highly sensitive "Know Your Customer" (KYC) data. This included video interviews and passport scans belonging to thousands of job seekers who believed their privacy was a foundational priority.
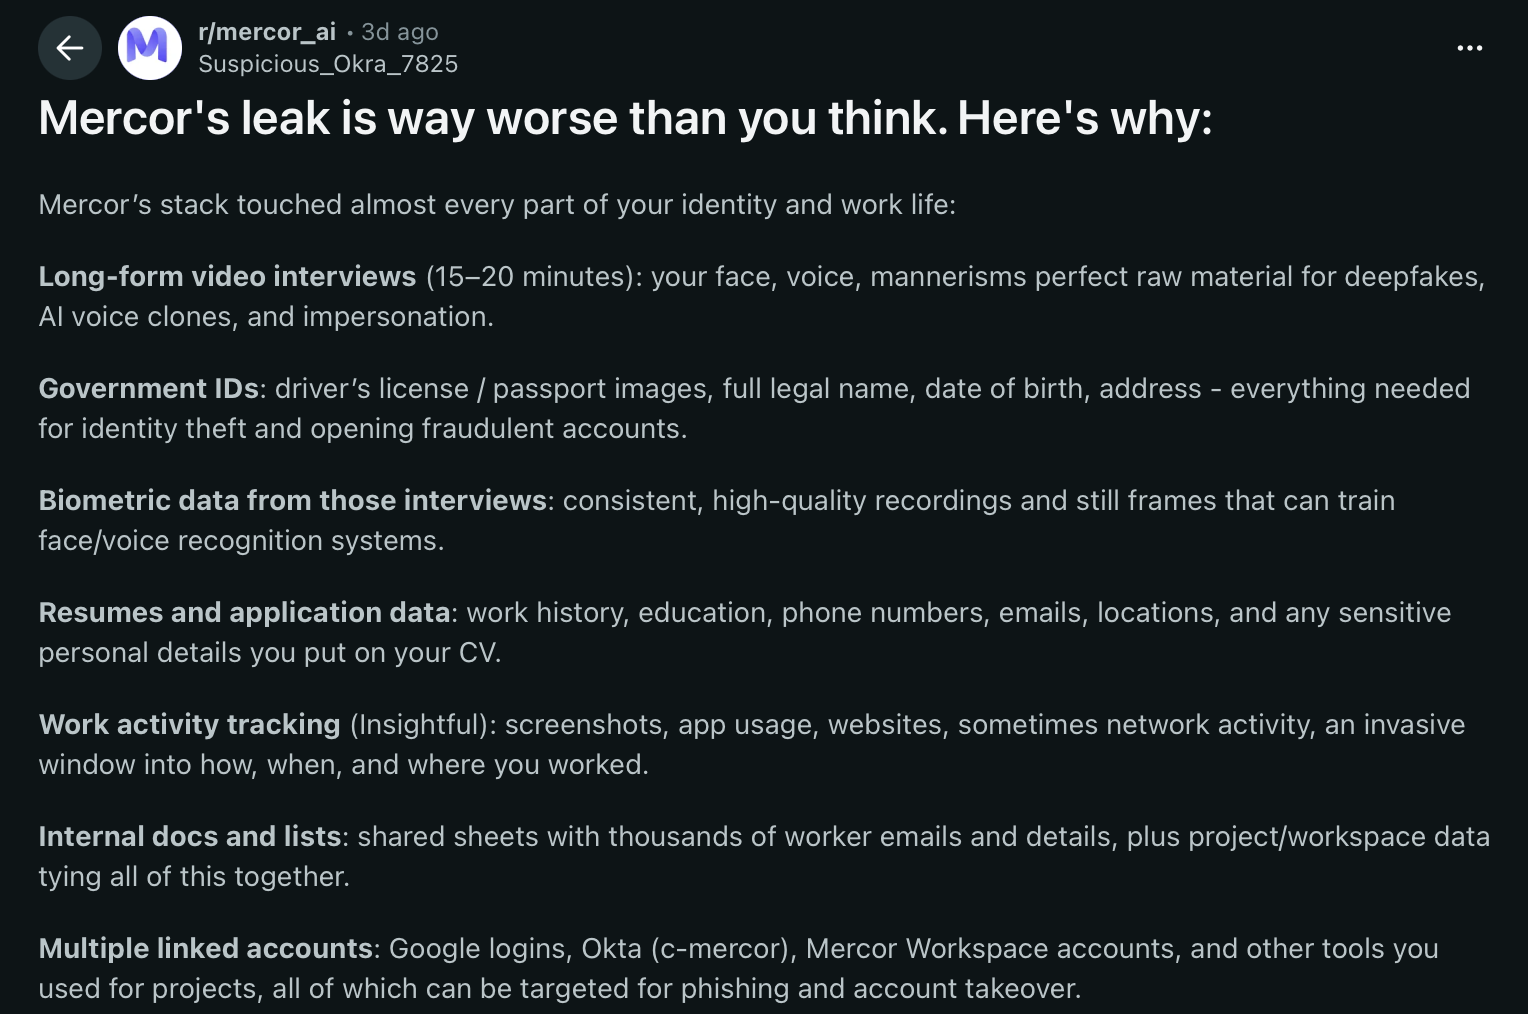
The most disturbing, if not unverified, glimpse into the company culture came from reports on social media. Internal screenshots allegedly leaked from the breach showed user interviews renamed with vulgar and unprofessional titles. It suggests an internal culture where the people being "AI-vetted" were viewed as data points or punchlines rather than human beings.
Furthermore, the presence of insightful monitoring software in the data haul raises systemic privacy alarms. These tools capture IP addresses, browser activity and sensitive personal metadata.
For a job seeker, the convenience of an AI platform now looks more like an invasive surveillance dragnet.
The Rise of "Vibecoding"
A recurring theme in this post-mortem is vibecoding.
Popularized in developer circles, the term describes a culture of rapid, AI-assisted development that prioritizes "vibe" and shipping speed over rigorous infrastructure. In a vibecoding environment, basic security hygiene is treated as a secondary concern.
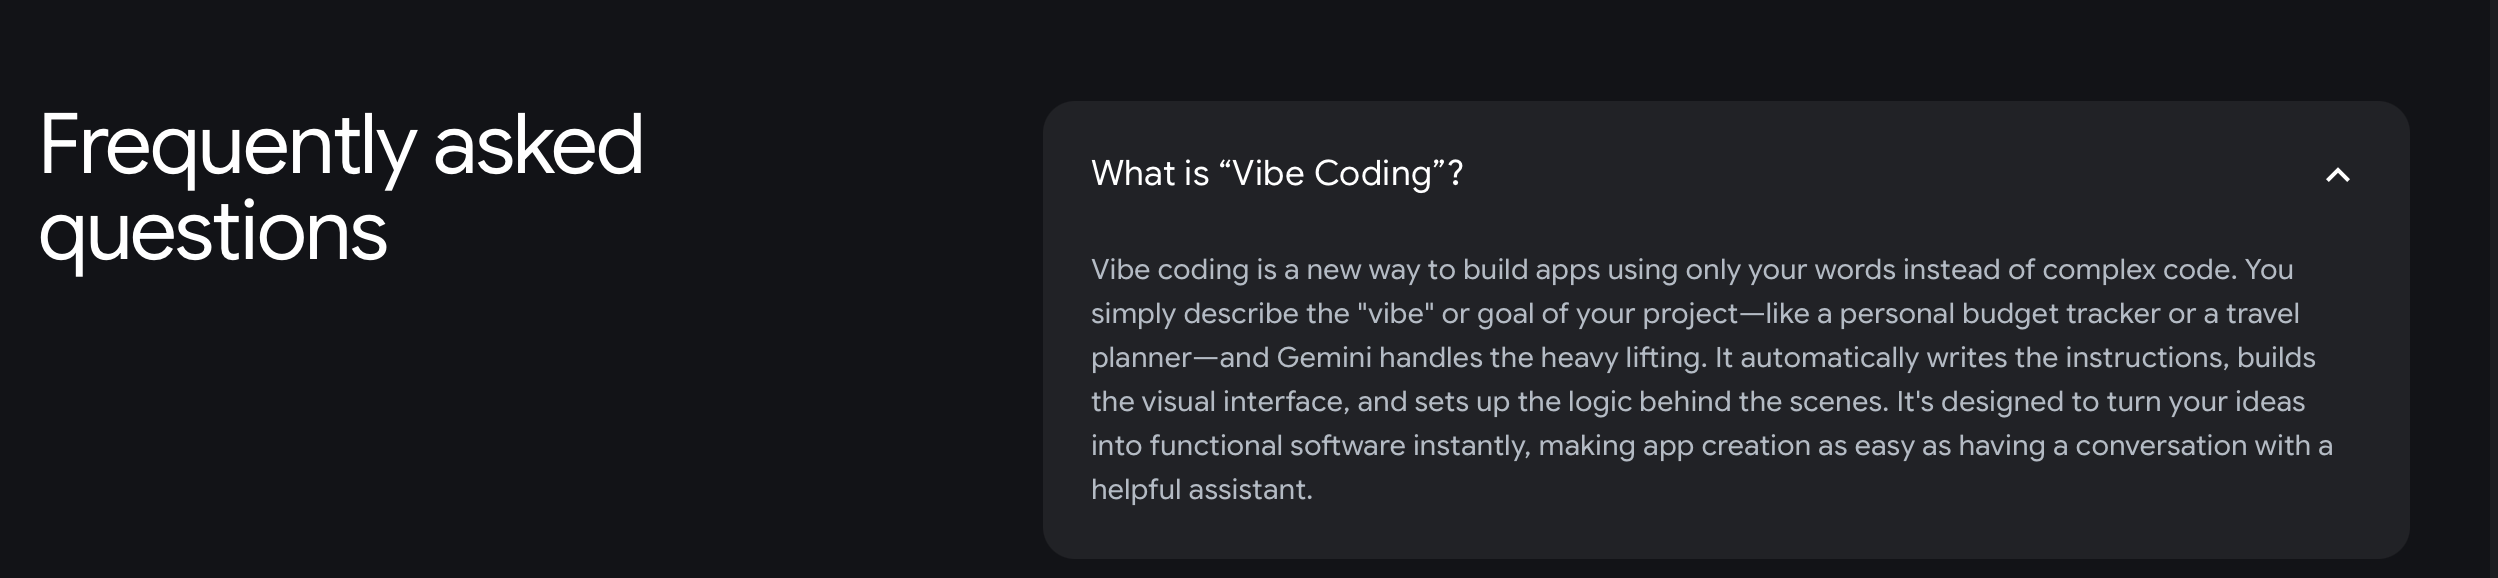
The technical evidence of this mindset was a catastrophic lack of isolation between development and production environments. When developers "move fast and break things," they often forget that the "things" being broken are the digital lives of their users. This governance failure provided a direct path for extortionists.
The consequences of this "vibe-first" approach are now being settled in dark web auctions. The Lapsus$ hacking group is reportedly auctioning the Mercor cache to the highest bidder. When a startup's growth outpaces its governance, it stops being a tech success story and starts being a high-value target for global extortion syndicates.
The New Era of Radical Transparency
The Mercor AI disaster serves as a definitive warning: a company’s security is only as strong as its least-known open-source dependency. We are entering a period of radical transparency, where a single 40-minute window can expose the inner workings and private data of a multi-billion-dollar enterprise.
The compliant shields of the past are proving insufficient against sophisticated upstream compromises. As our professional lives move further into the cloud, the risk to our digital identities becomes permanent and non-negotiable.
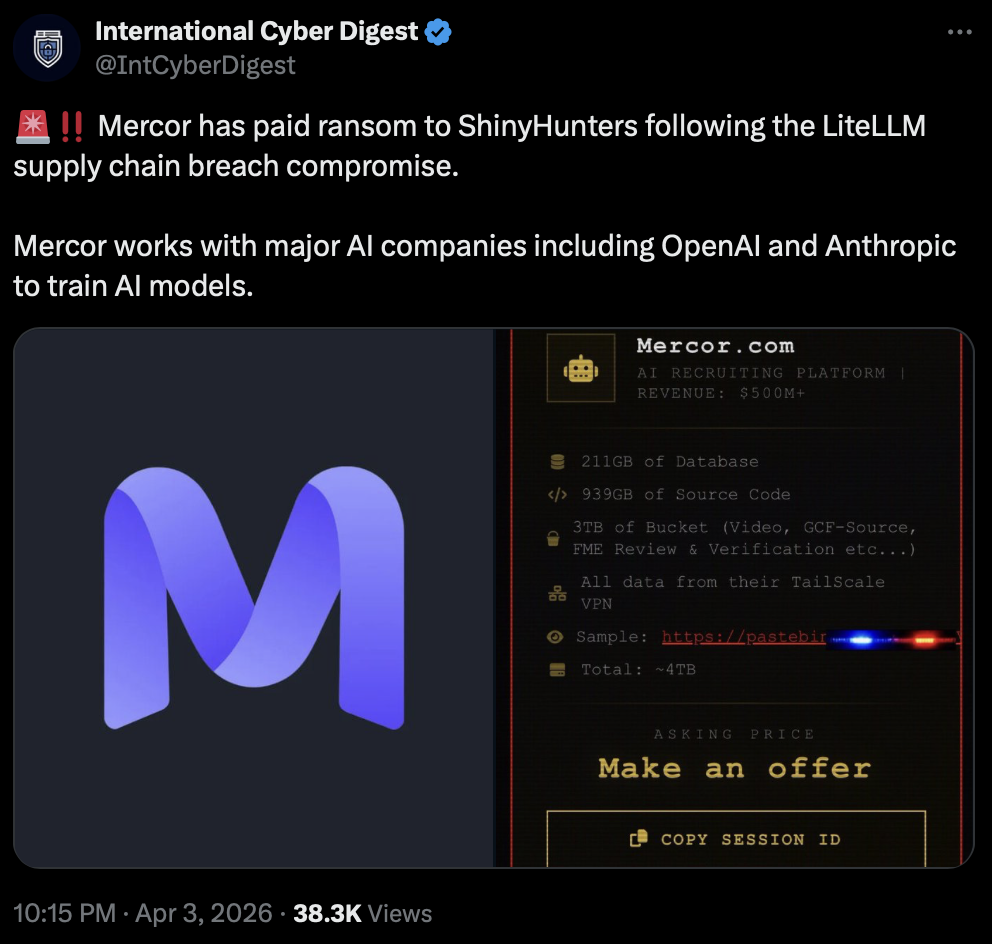
In an era where your video interview can be deepfaked and your passport is for sale on the dark web, is the convenience of AI-driven recruitment worth the permanent risk to your digital identity?
Sources
- 1https://www.founded.com/mercor-ai-youngest-self-made-tech-billionaires/founded.com
- 2https://research.contrary.com/company/mercorresearch.contrary.com
- 3https://www.scworld.com/brief/ai-startup-mercor-confirms-security-incident-linked-to-litellm-supply-chain-attackscworld.com
- 4https://www.cryptika.com/mercor-ai-confirms-data-breach-following-lapsus-claims-of-4tb-data-theft/cryptika.com
- 5https://exa.ai/websets/directory/mercor-fundingexa.ai
- 6https://bigthink.com/business/inside-the-meteoric-rise-of-mercor/bigthink.com
- 7https://www.mercor.com/blog/series-c/mercor.com
- 8https://www.softwareimprovementgroup.com/blog/litellm-supply-chain-attack/softwareimprovementgroup.com
- 9https://www.mexc.com/news/996309mexc.com
- 10https://www.trendmicro.com/en_us/research/26/c/inside-litellm-supply-chain-compromise.htmltrendmicro.com
- 11https://unit42.paloaltonetworks.com/teampcp-supply-chain-attacks/unit42.paloaltonetworks.com
- 12https://isc.sans.edu/diary/0isc.sans.edu
- 13https://beamstart.com/news/mercor-says-it-was-hit-17750091747526beamstart.com
- 14https://www.endorlabs.com/learn/teampcp-isnt-doneendorlabs.com
- 15https://www.securityweek.com/mercor-hit-by-litellm-supply-chain-attack/securityweek.com
- 16https://www.alibabacloud.com/blog/deep-analysis-the-litellm-supply-chain-poisoning-incident-%E2%80%94-a-full-link-analysis-of-the-teampcp-three-stage-backdoor_603001alibabacloud.com
- 17https://cybernews.com/security/mercor-data-breach-litelllm-supply-chain-attack/cybernews.com
- 18https://www.reddit.com/r/security/comments/1saaazf/ai_interview_startup_mercor_ai_has_reportedly/reddit.com
- 19https://www.reddit.com/r/mercor_ai/comments/1s8rppo/mercor_data_breach_update_insightful_is_affected/reddit.com
- 20https://www.reddit.com/r/mercor_ai/hot/reddit.com
- 21https://www.reddit.com/r/mercor_ai/comments/1s8jq3h/mercor_data_breach_is_this_legit/reddit.com
- 22https://www.reddit.com/r/recruitinghell/comments/1s82r3b/ahhhhhhhhhh/reddit.com
- 23https://www.reddit.com/r/mercor_ai/comments/1s93zz5/serious_question_do_we_actually_have_anything_to/reddit.com
- 24https://news.ycombinator.com/item?id=47596739news.ycombinator.com
- 25https://thecyberexpress.com/mercor-cyberattack/thecyberexpress.com
- 26https://hyper.ai/en/stories/08ac6ed649cfd7cf0773b679b9655d8fhyper.ai
- 27https://mlq.ai/news/ai-recruiting-platform-mercor-targeted-in-supply-chain-cyberattack-via-compromised-open-source-tool/mlq.ai